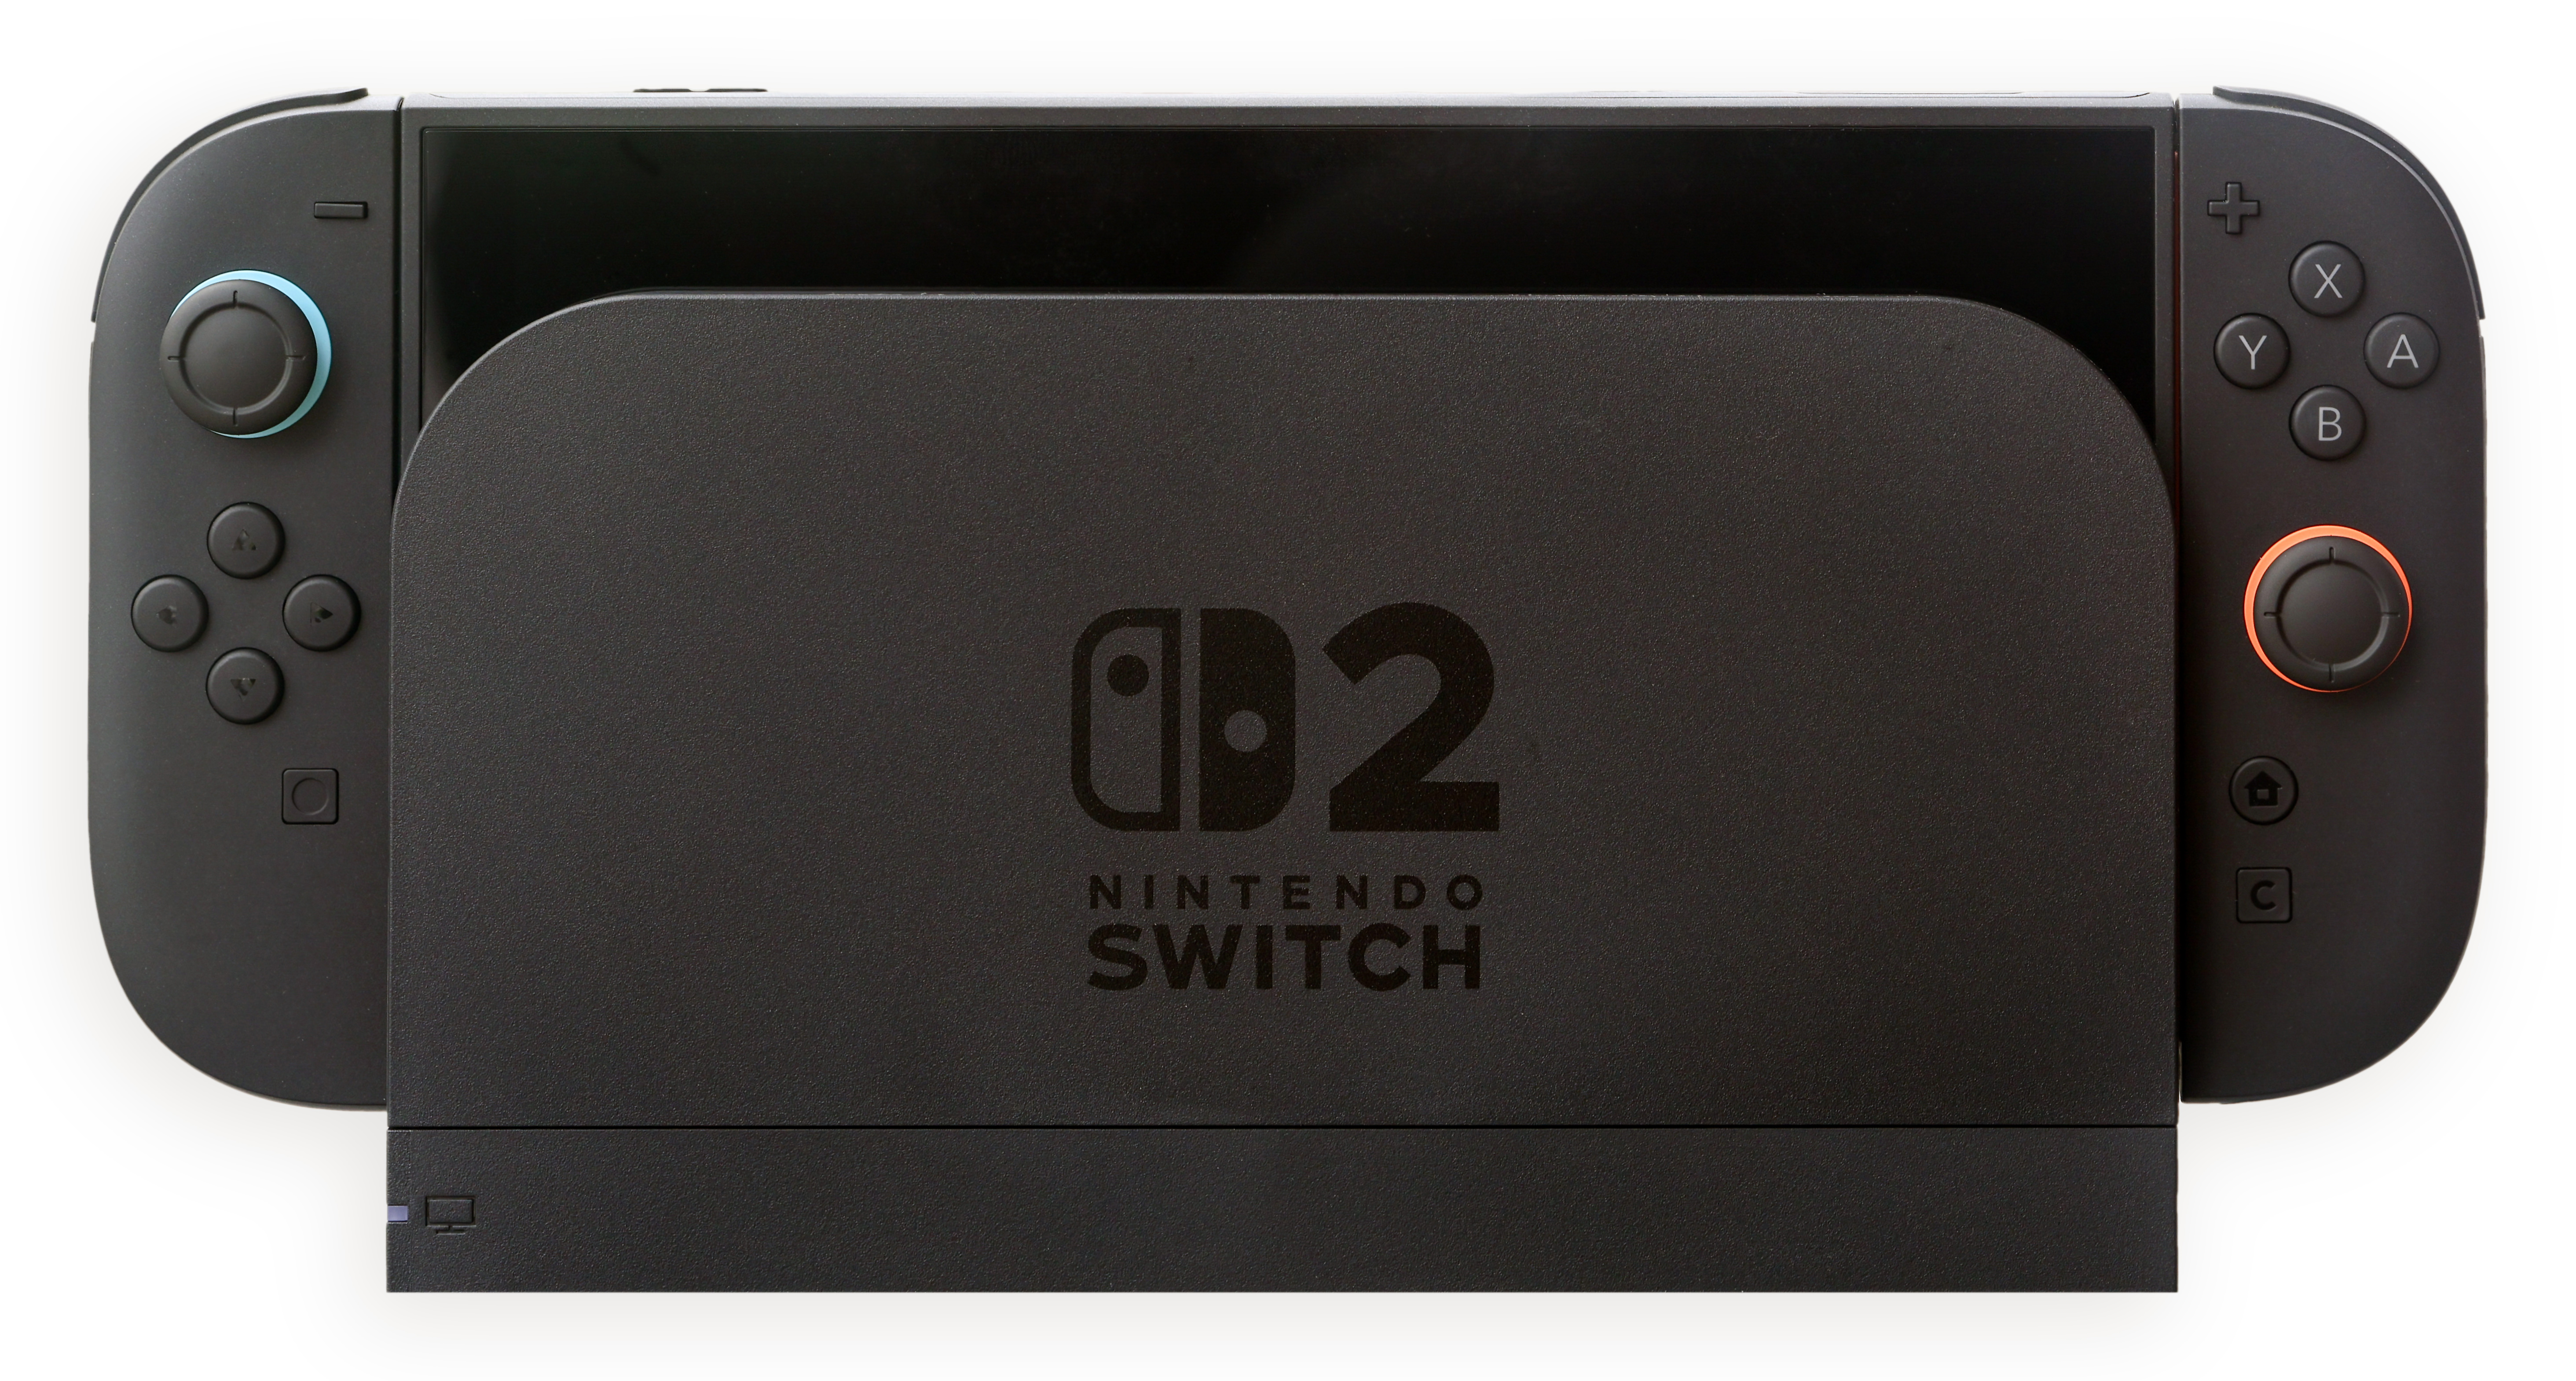
The Nintendo Switch 2 has been jailbroken for the first time. A proof-of-concept video published by security researcher Semmi Hajhamid (alias pepsipu) on October 22, 2026, shows a modified Mario Kart World running on the console: foreign characters — Cinnamoroll, a red Angry Bird, Peter Griffin, and Steve from Minecraft — have been added to the game. The researcher named the discovered exploit ns2jb. The Verge and Ars Technica covered the story.
How the Vulnerability Was Found
To find the vulnerability, Hajhamid used OpenAI's Codex AI coding tool. His approach was as follows: a specially prepared test program (harness) was written to automatically test the SmileBasic 4 programming language interpreter, while Codex helped in the process with writing and analyzing code. After almost two weeks of continuous work, the test program discovered the vulnerability — a 32-bit integer overflow that occurs when an element is removed from an array.
An integer overflow is a classic software bug in which a program exceeds the bounds of allocated memory during computation. In this case, the bug enabled reading and writing a certain portion of system memory — that capability became the foundation of the jailbreak. In other words, the researcher gained a way, albeit limited, to directly influence the console's protected memory regions.
"Hajhamid tested the SmileBasic 4 language interpreter using OpenAI's Codex AI coding tool, and after almost two weeks of work his specially prepared test program found a 32-bit integer overflow that occurs when an element is removed from an array — this allows reading and writing part of the system memory." — Ars Technica
Notably, the vulnerability was found with the involvement of an AI tool: Codex did not write the exploit on its own, but it significantly sped up the researcher's work of building the test infrastructure and analyzing code. This is being noted as one of the first public cases of a console's security being broken with the help of AI.
What ns2jb Enables
ns2jb is a software-only userland exploit. That means using it requires no opening the console, soldering chips, or physical interference with the hardware — everything is done in software. While the exploit does not give full control over the system's deepest layers, it unlocks the following practical capabilities: running unauthorized homebrew programs, reverse-engineering and modifying (modding) Switch 2 games, copying game save files off the console, and accessing most external devices via the MMIO interface.
"The software userland exploit allows running homebrew programs, reverse-engineering and modding Switch 2 games, backing up saved files from the console, and accessing most external devices via MMIO." — Ars Technica
In other words, ns2jb opens the door to using the console beyond the boundaries set by the manufacturer: independent developers can test their apps, modders can alter game content, and researchers can study the system's inner workings. The exploit operates at the userland level — that is not full control over the system's deepest layers, but it is a sufficient level for homebrew programs and game mods.
The Proof Video
To prove the exploit works, Hajhamid published a video on October 22, 2026. The video shows the modified Mario Kart World running on the Switch 2 hardware itself — on screen, instead of the game's original characters, Cinnamoroll, a red Angry Bird, Peter Griffin, and Steve from Minecraft appear. These frames confirm that ns2jb is not a theoretical vulnerability but a working exploit on a real console.
The video was covered by The Verge, which presented it as the console's first public jailbreak.
Limitations
However, this is considered a "tethered" hack and has a serious limitation: to run the exploit, a node.js package must be running on a macOS or Linux computer on the same network as the console. In other words, activation via an external computer is required each time — the console itself does not persist the exploit on its own. In practice, this means the user must connect the console to a computer and run a special command every time.
Still, this is a significant turning point for the Switch 2 ecosystem: unauthorized code was run on the console for the first time, and it happened through a vulnerability found with the help of an AI tool. The next steps — the spread of the exploit as public tools and the manufacturer's response — remain unknown for now.