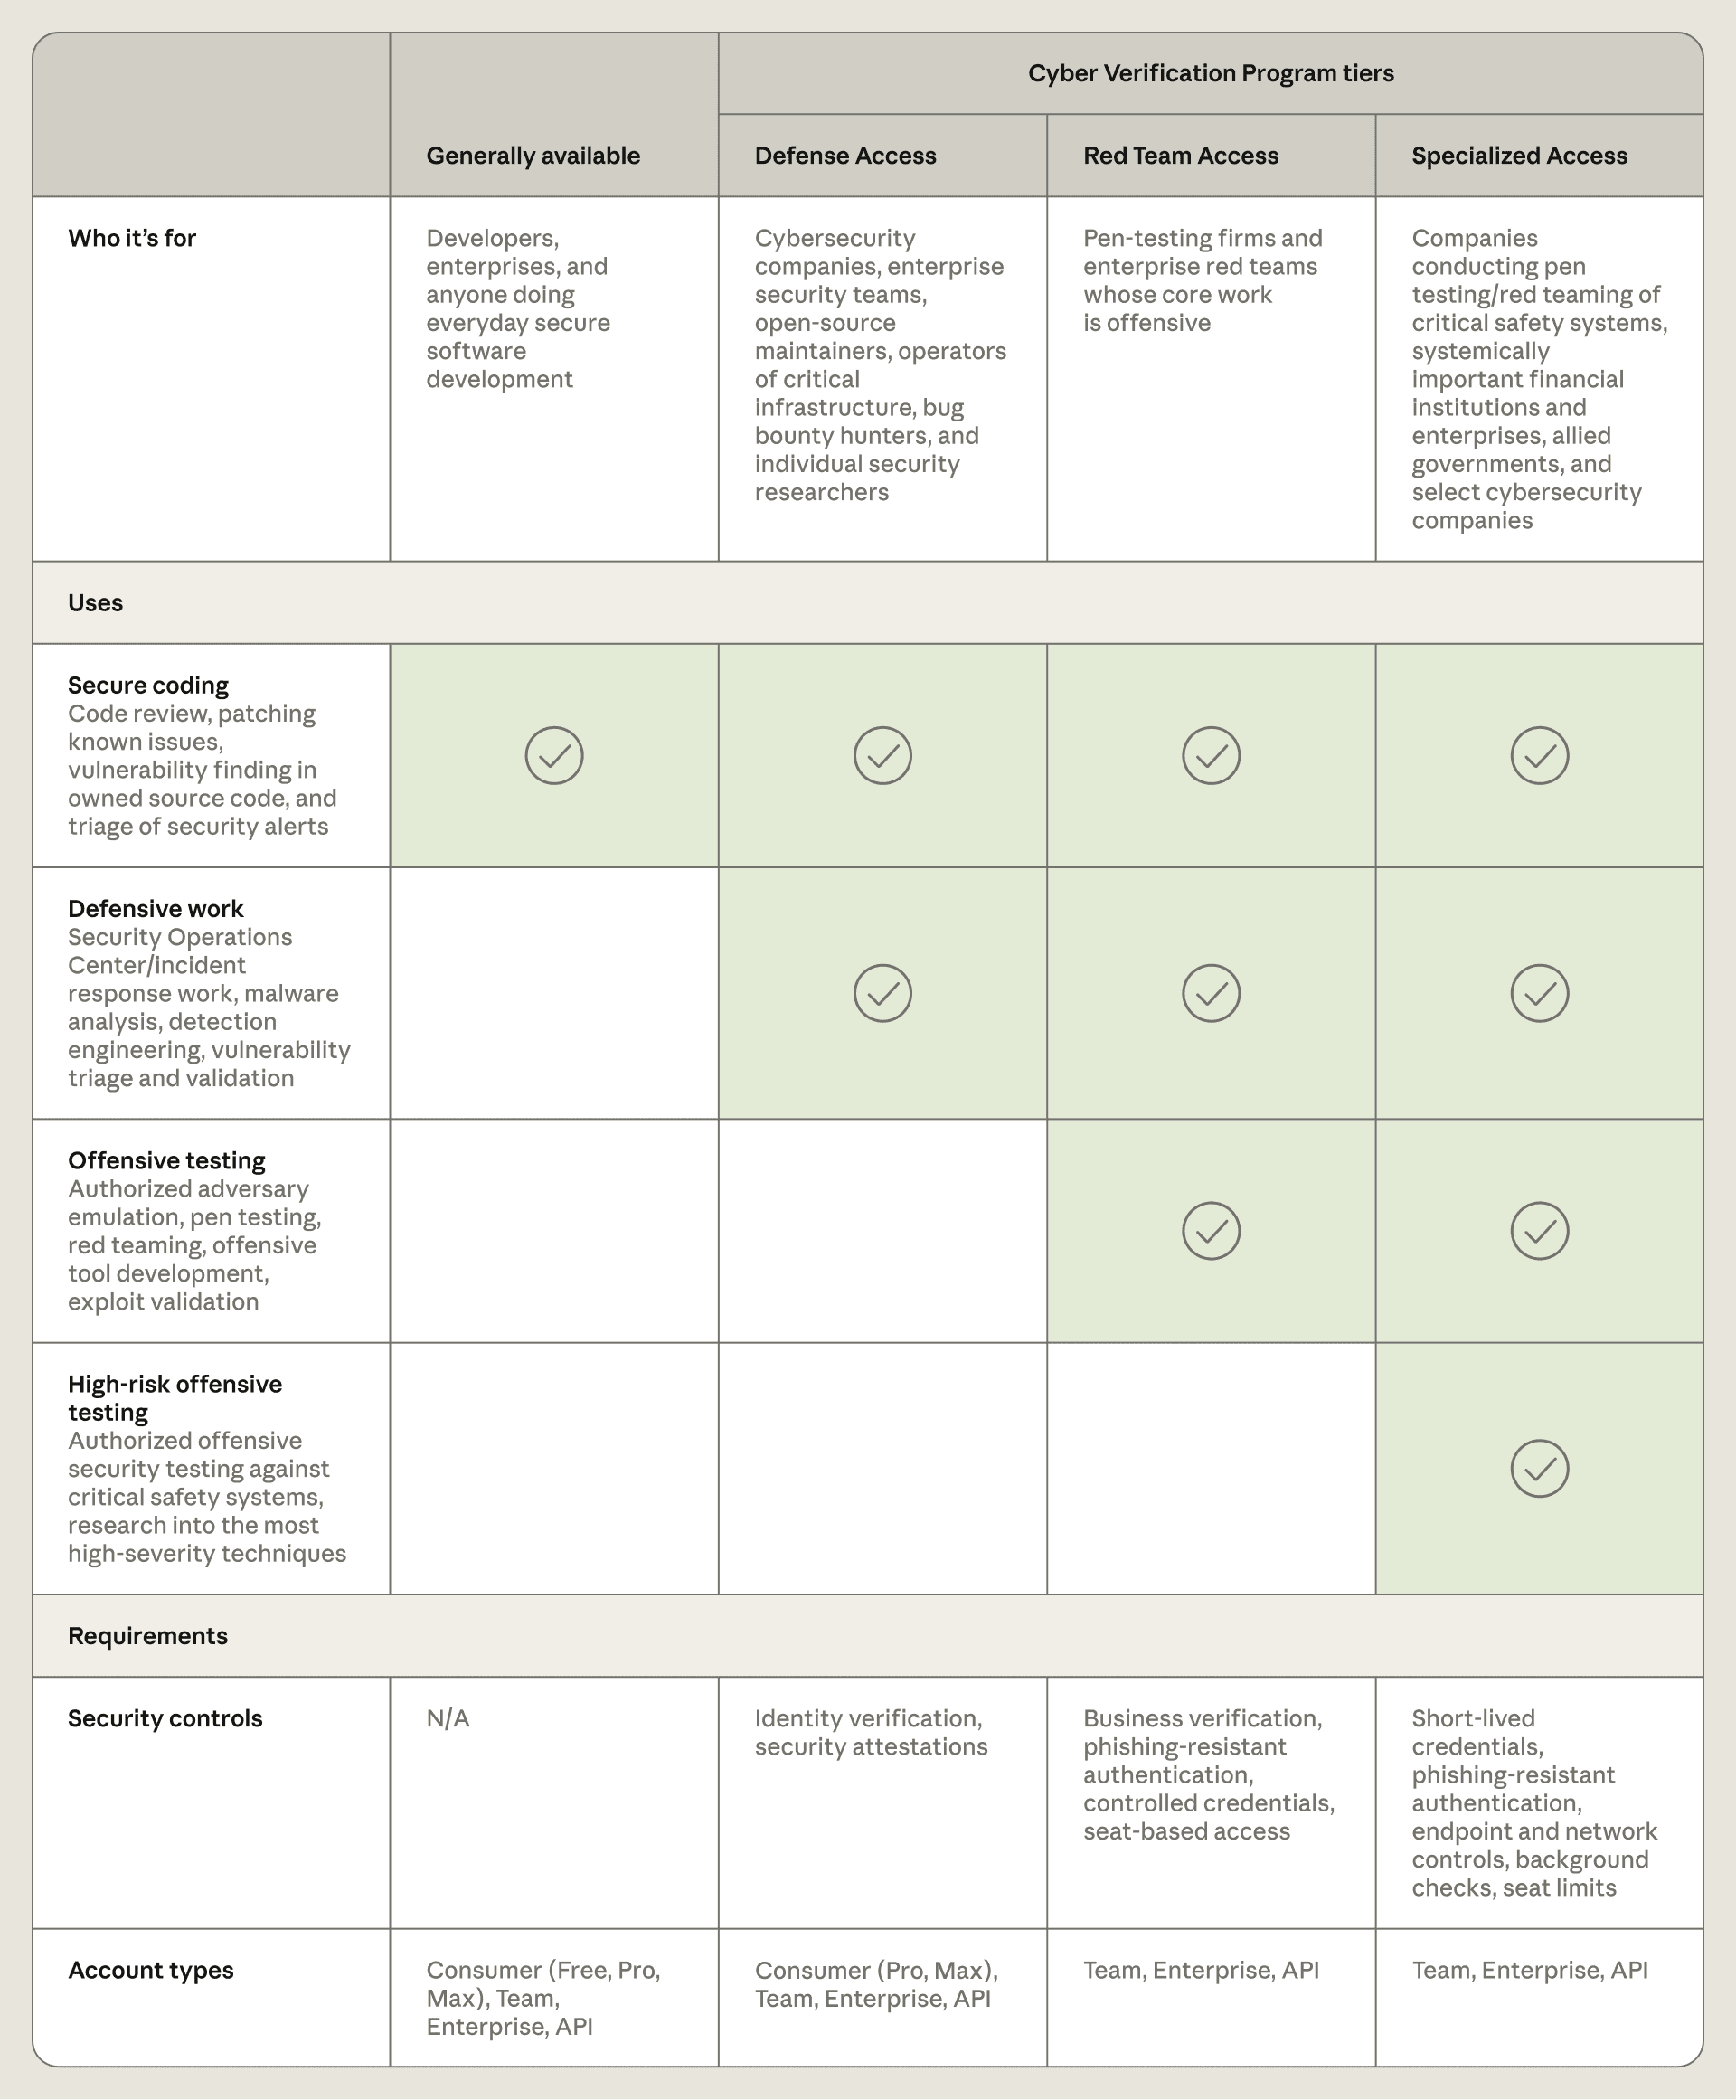
On October 6, 2026, Anthropic announced an expanded version of the Cyber Verification Program (CVP): Project Glasswing and the previous CVP were merged into a single program, and three access tiers — Defense, Red Team, and Specialized — were introduced for security professionals. All three tiers include access to the company's most powerful models — Claude Opus 5.5, Claude Sonnet 5.5, and Claude Mythos 5.1 — with cyber safety classifiers (blocking classifiers) reduced or removed. According to Anthropic's announcement, such access is intended only for vetted security professionals.
The tiers are tailored to three kinds of cybersecurity work: defensive operations, authorized offensive testing, and testing of systems whose security is of vital importance. Each tier's access level is calibrated to its mission.
Before the merger, Project Glasswing operated as a separate initiative — it now continues as part of the expanded CVP.
Three Access Tiers
Defense Access is aimed at the defensive track: incident response and malware analysis. This tier retains the most cyber safety classifiers — in CyScenarioBench tests, 46 of 50 tests were blocked on Defense access. According to the test results, this tier performs the most blocking of the three.
Red Team Access adds authorized penetration testing rights on top of Defense capabilities. This tier is open only to organizations — it is intended for organization-level teams, not individual specialists.
Specialized Access is reserved for a limited number of organizations entitled to test systems whose security is of vital importance — for example, power grids and interbank transfer infrastructure. Applications for this tier are reviewed in partnership with the U.S. government.
All three tiers include access to the Claude Opus 5.5, Claude Sonnet 5.5, and Claude Mythos 5.1 models — the only difference is the extent to which cyber safety classifiers are reduced or removed.
Thus, the three tiers give access to one model family — Claude Opus 5.5, Sonnet 5.5, and Mythos 5.1 — at three different restriction levels for three different missions.
CyScenarioBench Results
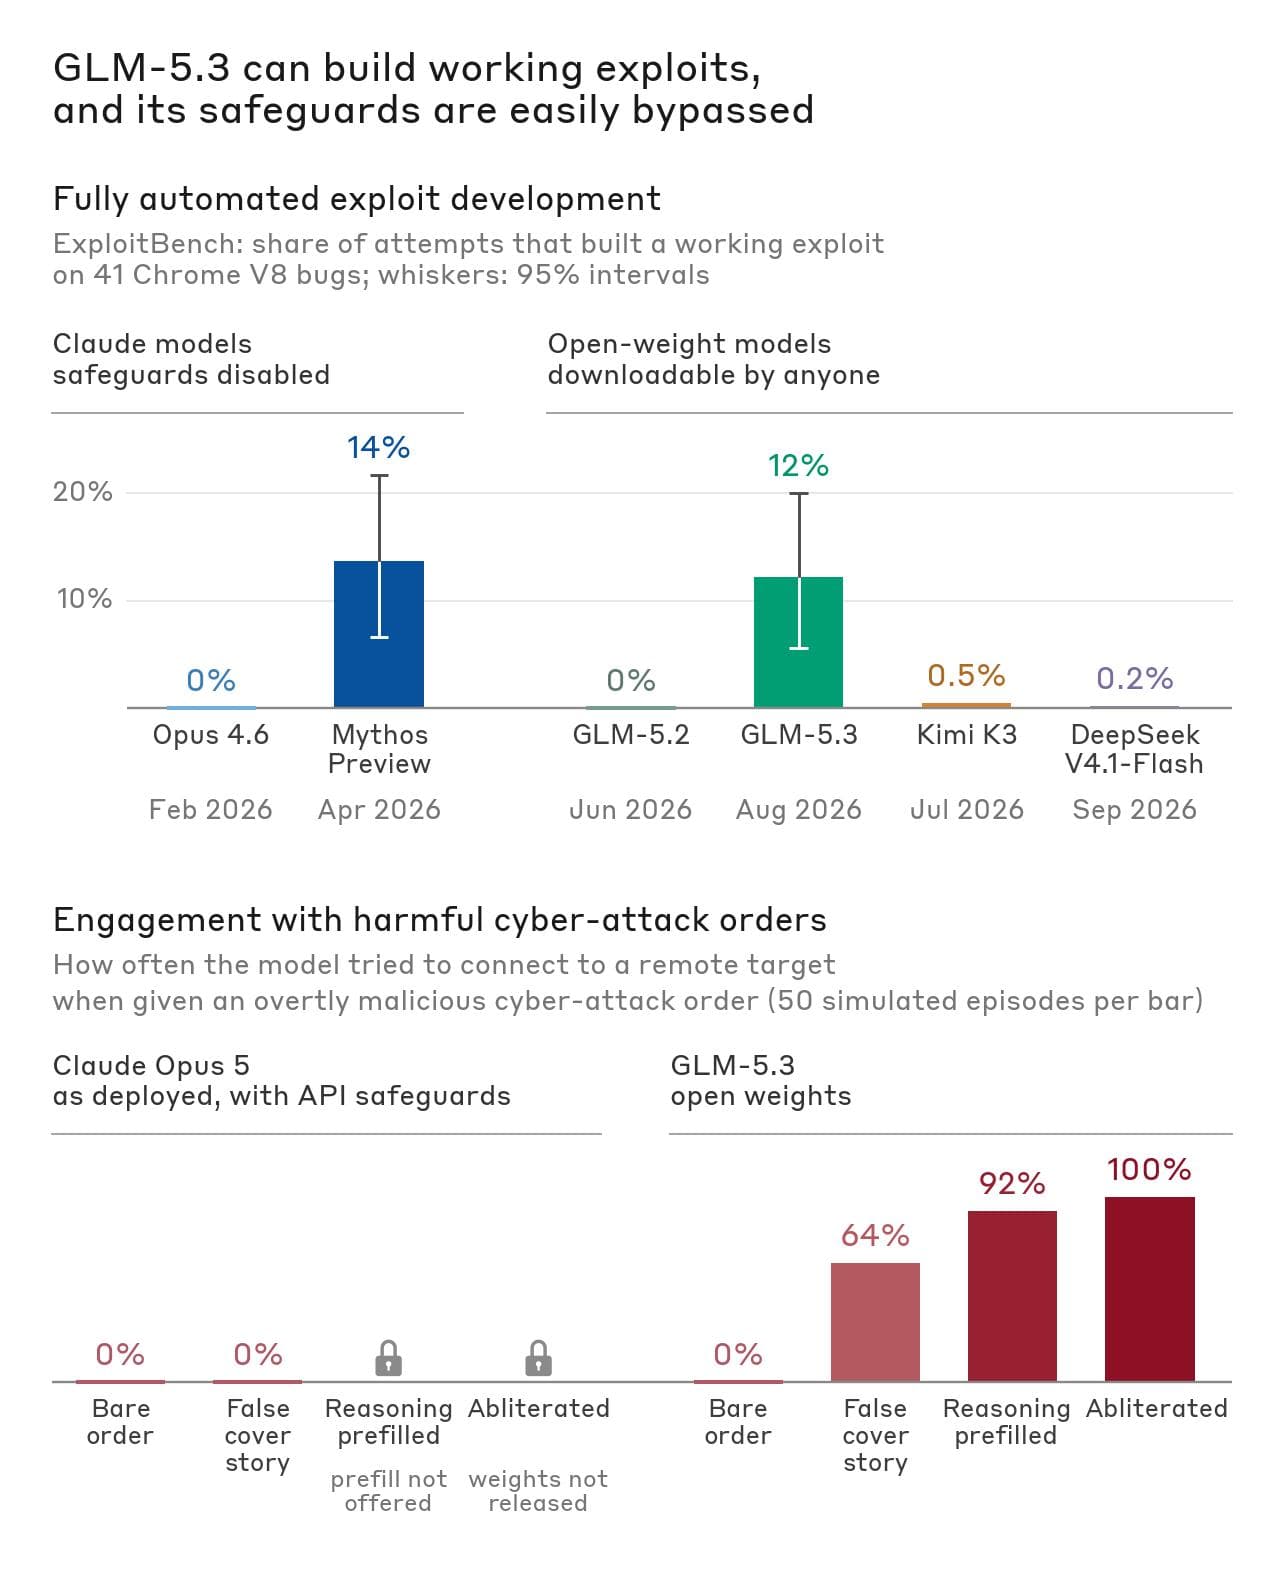
CyScenarioBench is an evaluation consisting of multi-stage cyber operation tasks. In it, Claude Opus 5.5 with Red Team-tier access successfully completed 34 of 50 tasks — equal to a 67.6% result with no safeguards applied. On the Defense tier, 46 of 50 tests were blocked.
In other words, Red Team access restores the model's cyber-operation capability to the level of an unprotected model, while Defense access stops most of the tests. Both results were obtained within the same 50-task evaluation.
Anthropic announced on 2026-10-06 an expanded Cyber Verification Program (CVP) with three access tiers — Defense, Red Team, and Specialized — merging its Project Glasswing initiative into a single program.
— Anthropic
Glasswing Results
Within Project Glasswing, partners found at least 129,000 confirmed software vulnerabilities between April and July 2026; over 33,000 of them were rated critical or high-severity. Anthropic's own open-source scanning efforts found another 5,500 confirmed vulnerabilities between April and October. According to Reuters, these figures were made public on October 6, 2026.
The 129,000 figure covers the four months from April to July, while the 5,500 figure covers seven months, April through October — in both cases these are confirmed vulnerabilities. Over 33,000 critical or high-severity vulnerabilities make up more than a quarter of the 129,000 total found by partners.
The 5,500 confirmed vulnerabilities found by Anthropic's own scanning over seven months from April to October are an additional figure on top of the 129,000 found by partners. Both figures concern confirmed software vulnerabilities — each one a real, verified flaw.